The real question
Your scanner finds the gaps faster. Who helps the supplier close them?
What works
Your top tier, roughly 5 per cent of most supplier lists, carries ISO or SOC 2 and answers your questionnaires. Keep doing that.
Where the other 95 per cent fall through
Questionnaires were built for enterprises, not a three-person supplier, so they take your team weeks and still rely on what suppliers say about themselves. Scanning and ratings find small suppliers’ gaps faster than ever, but can’t help them close one.
What’s missing
A pathway built for the supplier: certification proportionate to their size, certified providers to help, and a public register you check in seconds. That’s SCAP, the Supplier Cyber Assurance Program, alongside whatever you already run. It costs your organisation nothing.
SMB1001 · Dynamic Standards International · certified by CyberCert
What you’ll see
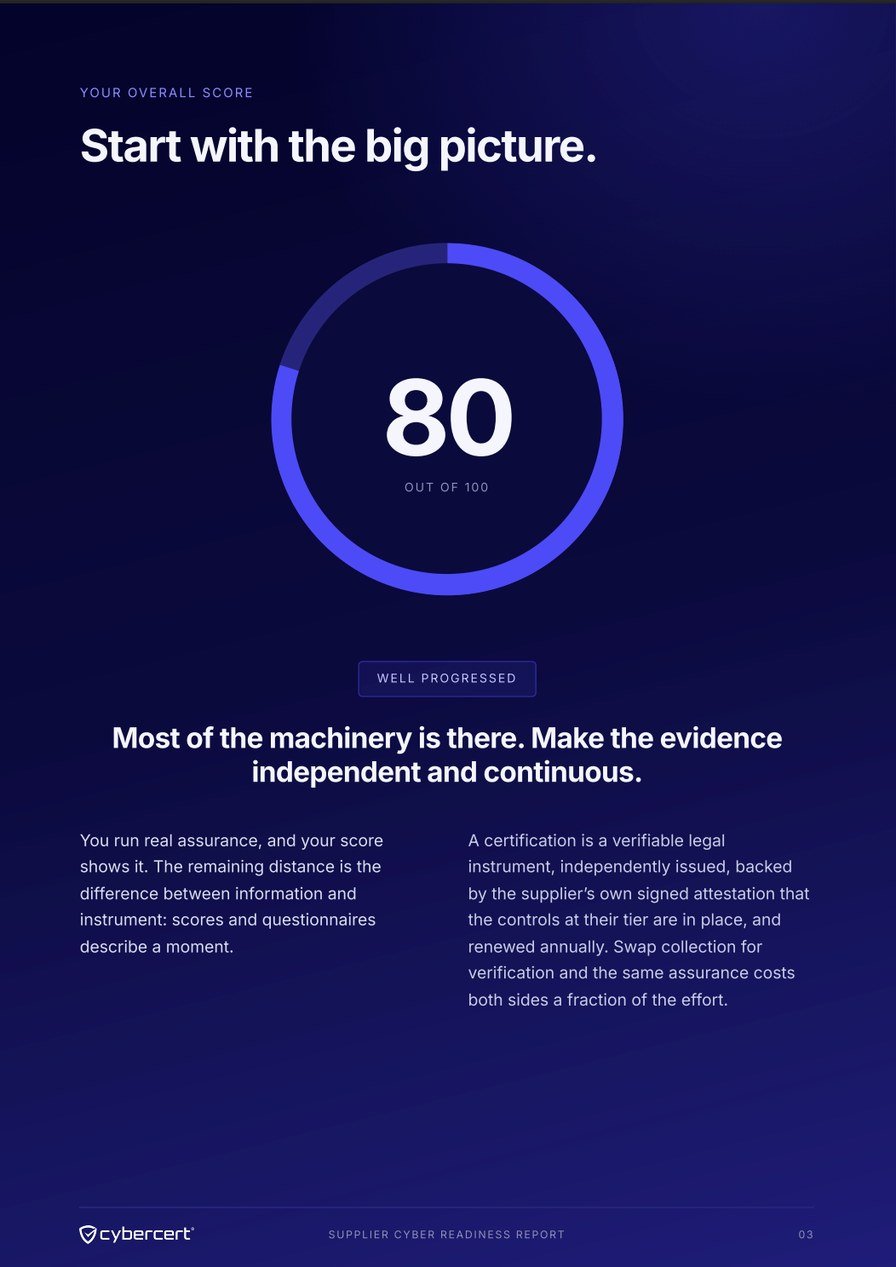
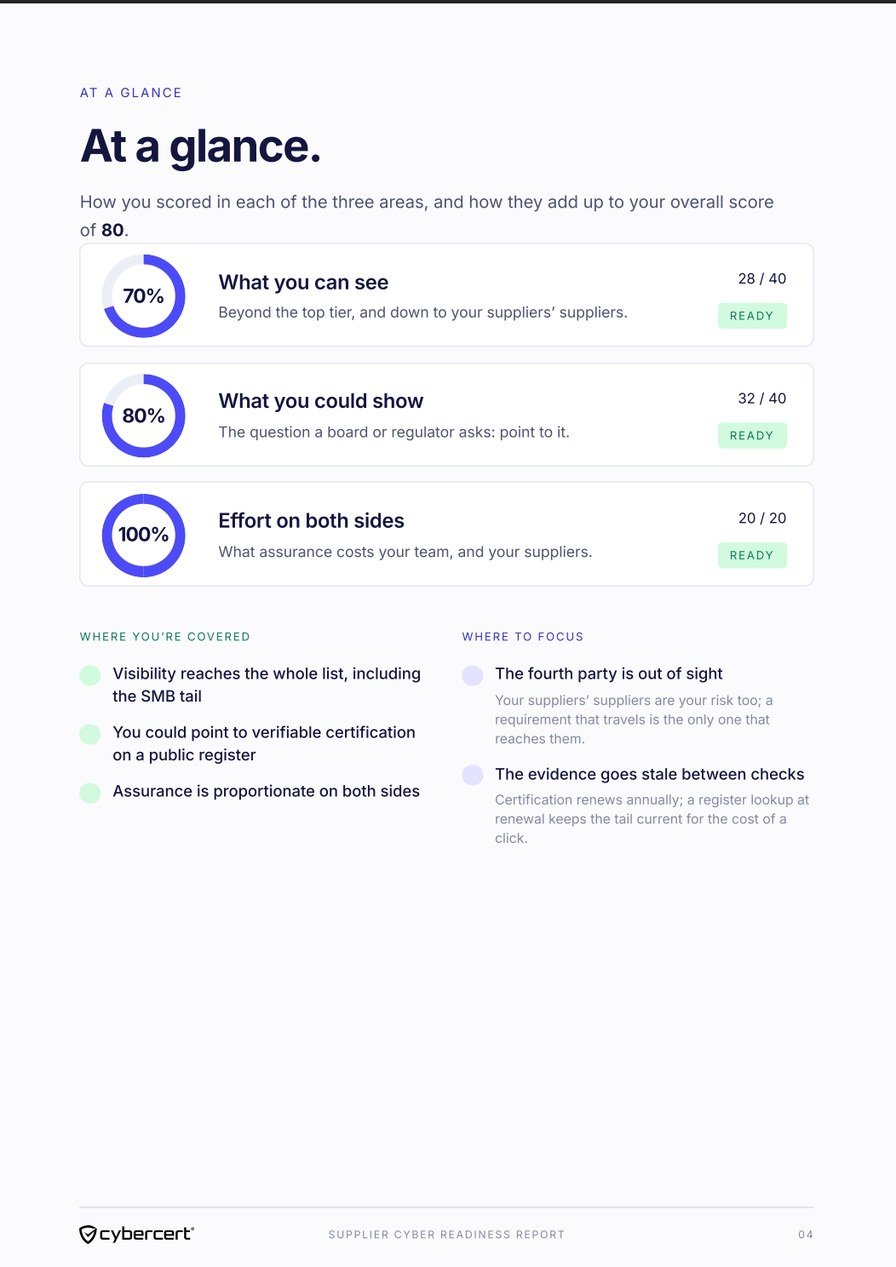
Your score across the three things that decide your supply chain risk.
No technical questions and nothing to prepare. Just the honest state of play: what you can see, what you could show, and the effort on both sides. We never publish or sell your answers. See our privacy policy. Your report names where you’re covered, where you’re exposed, and the plain-English reason each one matters.
Inside your report
Ten pages, written for your answers.
After your score
Help the SMBs help you.
01
Take the check, free.
Three minutes. Your Supplier Cyber Readiness Report is ready to download straight away.
02
Download the free SCAP Activation Toolkit.
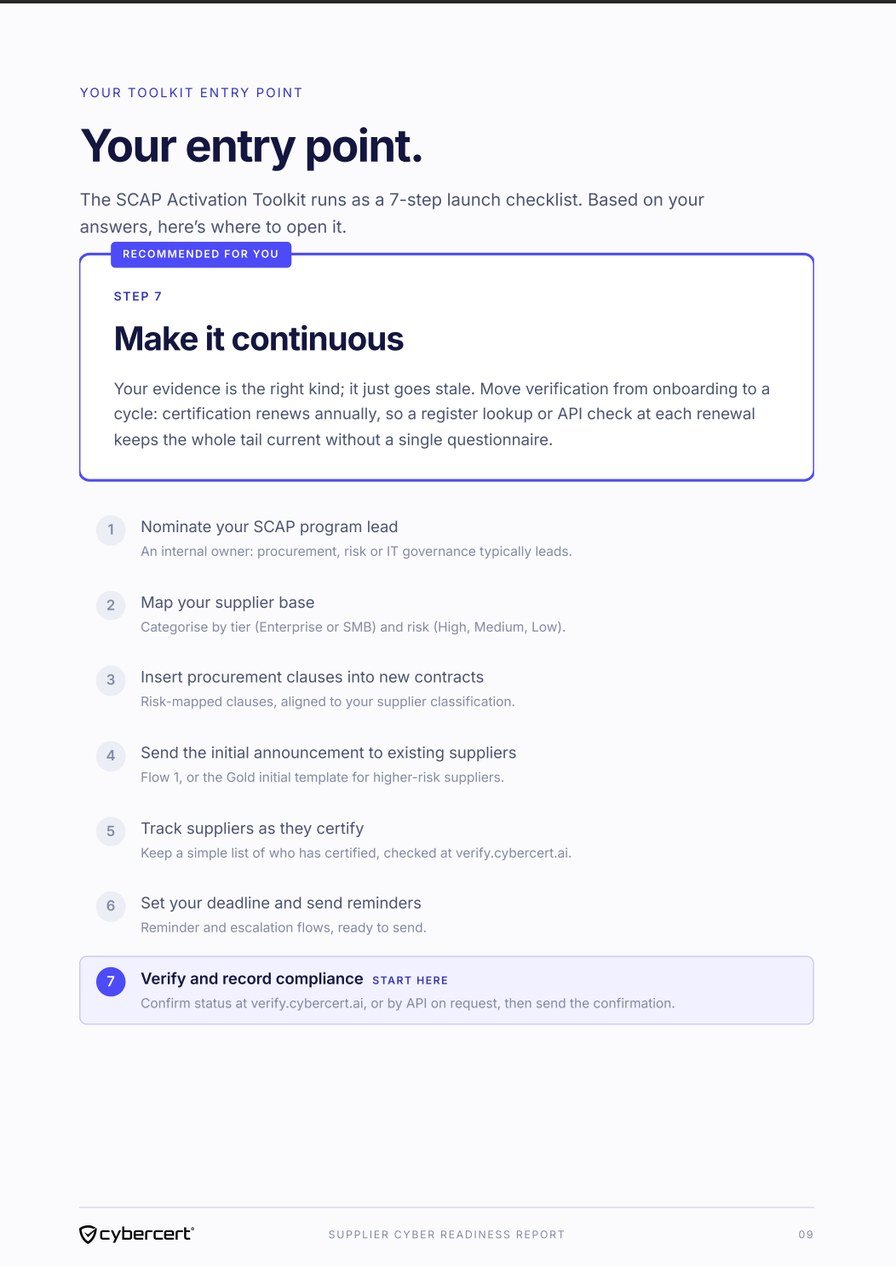
Supplier segmentation, risk-mapped contract clauses, ready-to-send emails and a 7-step launch checklist. Built to run with your existing platforms and processes, not replace them. scap.cybercert.ai/scap-toolkit
03
Verify, don’t collect.
Ask suppliers to show their certification, look any supplier up at verify.cybercert.ai, or, on request, connect it to your own systems by API. Nothing new to buy, nothing to deploy.
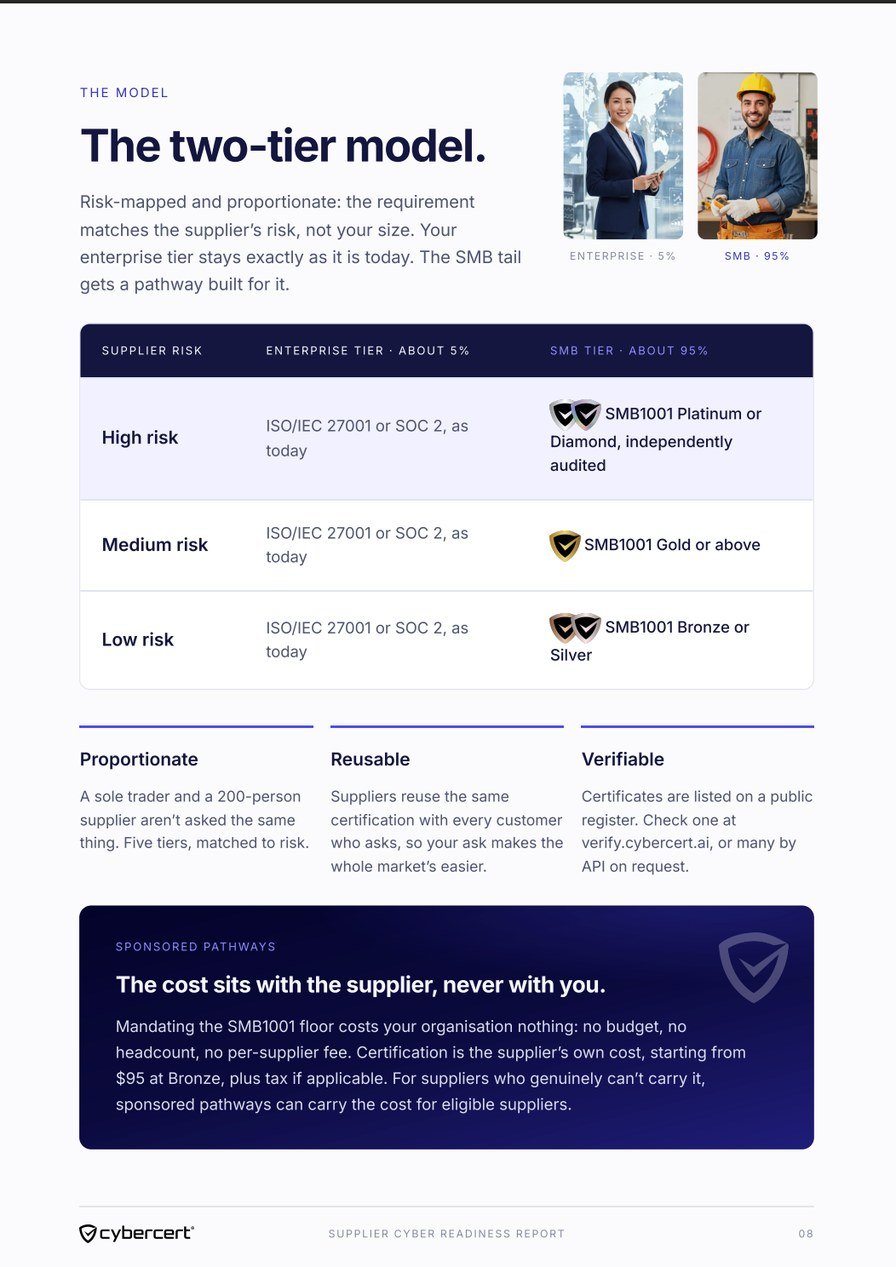
The model
High risk · SMB supplier
SMB1001 Platinum or Diamond, independently audited.
Medium risk · SMB supplier
SMB1001 Gold or above.
Low risk · SMB supplier
SMB1001 Bronze or Silver.
Enterprise tier · about 5%
ISO/IEC 27001 or SOC 2, as today.
Risk-mapped and proportionate: the requirement matches the supplier’s risk, not your size. Suppliers reuse the same certification with every customer who asks, so your ask makes the whole market’s easier.